There is no universal certification package that makes every smartwatch ready for every market. Smartwatch certification requirements depend on where the product will be sold, which radios and battery it uses, how it is charged, its intended use and the claims made about it. A Bluetooth-only consumer watch and a cellular safety wearable can therefore follow very different paths. Buyers should define the applicable obligations before hardware is frozen—not request a generic folder of certificates after production has started. Early planning reduces the risk of testing the wrong configuration, overlooking market-specific requirements or repeating work after a component change.
Start With the Product Configuration and Target Market
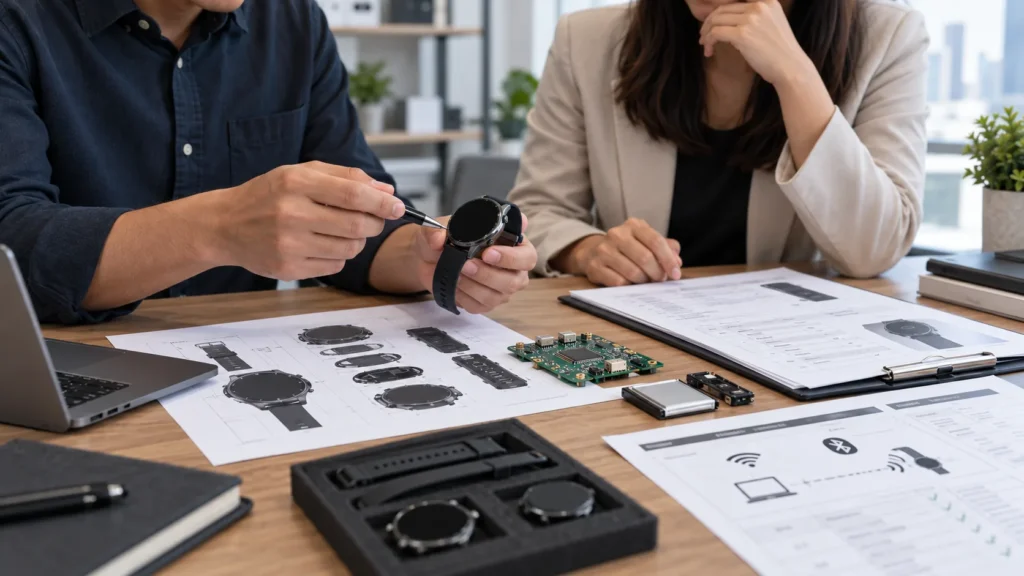
Certification planning begins with a controlled product definition. A report for a related watch, radio module or battery does not automatically cover the configuration being purchased. Before asking which documents are needed, record:
- the countries or regions where the watch will be marketed;
- the exact model and hardware revision;
- Bluetooth, Wi-Fi, GNSS and cellular radio configurations;
- the cellular module, antenna arrangement, SIM or eSIM approach and supported bands;
- the battery cell, pack design and charging method;
- the intended users, operating environment and service workflow;
- all safety, wellness, health or medical claims; and
- whether the project uses a standard model or customized hardware, firmware, enclosure or branding.
This configuration record should be shared by engineering, compliance, sourcing and the supplier. It also gives a smart watch OEM/ODM development team a stable basis for identifying tests, documents, samples and change controls. If the specification changes, the team can assess the affected approvals instead of assuming that the original evidence still applies.
What Types of Smartwatch Compliance Requirements Should Buyers Consider?
The word “certification” is often used for several different obligations. Keeping the categories separate prevents a buyer from treating one document as proof of everything.
- Regulatory and market-access requirements concern whether a product may be placed on a particular market. The applicable route depends on the jurisdiction and product configuration.
- Radio conformity requirements address intentional transmitters and related technical characteristics. Bluetooth, Wi-Fi and cellular functions may affect the assessment.
- Cellular industry and operator requirements can sit alongside government regulation. A cellular device may need industry certification or operator acceptance where applicable, even when its radio module already has supporting evidence.
- Restricted-substance and chemical obligations may apply to electrical and electronic equipment, components, cables, straps, packaging or articles in the supply chain.
- Battery transport evidence supports the safe transport of lithium cells and batteries. It does not replace electrical, radio or product-safety assessment.
- Manufacturer quality-management systems concern how an organization controls its processes. ISO 9001 or ISO 13485 certification, when relevant, is not a product market-access approval.
A defensible compliance file identifies which category each item belongs to, the exact product it covers and the party responsible for maintaining it.
What Does a Smartwatch Need for the US Market?
A smartwatch containing radio transmitters normally requires the applicable US equipment-authorization route before it is marketed or imported. The correct route and filing depend on the device and radio functions, so buyers should confirm the requirements for the complete watch rather than rely only on a Bluetooth or cellular module certificate.
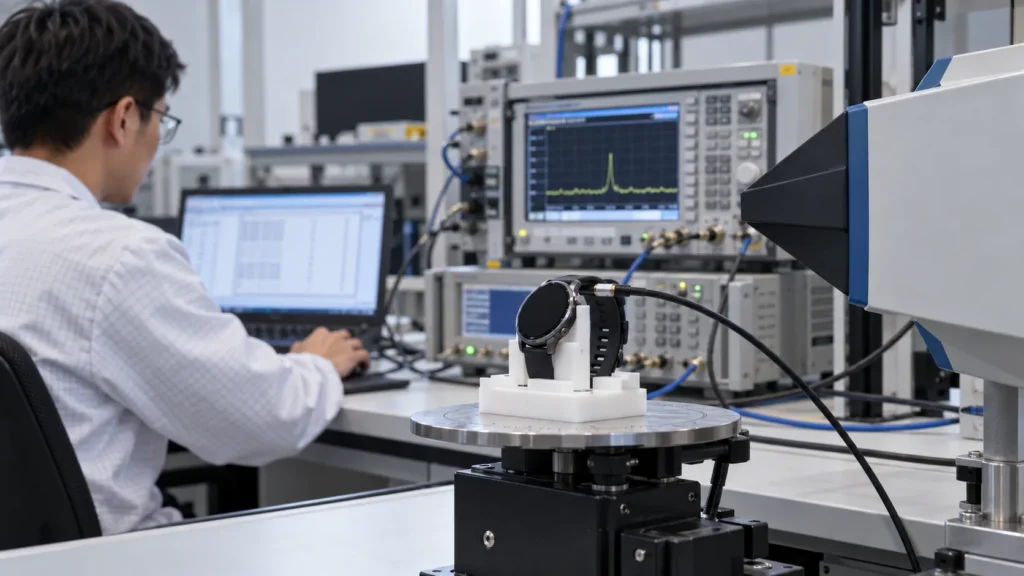
For an FCC-related review, request the identifiers and reports for the exact product configuration. Check that model names, hardware versions, radio bands, antennas and grant conditions align with the unit being supplied. A certified module can be useful evidence, but integration details—including the antenna, enclosure, simultaneous transmissions and labelling—may still affect the host product assessment.
Because a smartwatch is a body-worn RF device, the FCC review should also confirm the applicable RF-exposure evaluation for the final product configuration rather than relying only on radio-module authorization. The appropriate evaluation depends on the device and its operating conditions; this should not be read as a universal requirement for one particular test method.
Cellular projects need a separate network-readiness review. PTCRB certification may be applicable to a cellular watch intended for participating North American networks. The route can depend on whether the design integrates a certified module and on the final device configuration. An operator may also impose its own acceptance or technical requirements. FCC authorization, PTCRB certification and operator acceptance are therefore related but not interchangeable checks. None should be presented as proof that the watch will perform equally on every operator, SIM profile or coverage environment.
What Does a Smartwatch Need for the EU Market?
For a wireless smartwatch placed on the EU market, the Radio Equipment Directive is commonly central to the conformity assessment. The manufacturer is responsible for identifying the applicable requirements, completing the appropriate assessment, compiling technical documentation, issuing an EU Declaration of Conformity and affixing the CE marking when conformity has been demonstrated.
CE marking should not be treated as a certificate that can simply be purchased from a laboratory. Test reports may support the assessment, but the manufacturer must connect the evidence to the final product and its intended use. Buyers should check the declaration, referenced standards, model identity, radio configuration and technical-file coverage rather than accept a CE logo or an unrelated certificate at face value.
For internet-connected or other relevant wearable radio equipment, EU planning should also review the currently applicable cybersecurity-related RED requirements under Article 3(3)(d), (e) and (f). Depending on the device functions and intended use, these provisions may address protection of networks, safeguards for personal data and privacy, and protection from fraud. Delegated Regulation (EU) 2022/30 applies these requirements to specified categories of radio equipment until 10 December 2027; the Cyber Resilience Act framework applies in full from 11 December 2027. Teams should therefore confirm the scope against the product, placing-on-the-market date and regulatory framework then in force.
EU planning may also include RoHS restrictions for electrical and electronic equipment and applicable REACH supply-chain obligations. Their relevance and required evidence depend on the product, materials and role of each economic operator. A supplier declaration can be part of the file, but buyers should define which components and materials it covers and how changes will be controlled.
What Battery Documents Should Be Reviewed?
The battery file should match the cell or battery installed in the production watch. For lithium batteries, buyers commonly request the relevant UN 38.3 test summary and supporting identification. Review the manufacturer, model, electrical characteristics and physical configuration against the bill of materials and product sample. Evidence for a similar cell is not a reliable substitute.
Transport arrangements also depend on whether batteries are shipped alone, with equipment or installed in equipment, as well as the transport mode and logistics route. The compliance team or logistics provider should determine the applicable packaging, marking and documentation. If the battery, pack protection circuit, capacity, supplier or construction changes, assess whether the existing evidence remains applicable before shipment.
Battery transport documentation is only one part of the project. It should not be presented as evidence that the charging design, runtime, thermal behaviour or complete watch is suitable for its intended service.
When Are Medical Device Requirements Relevant?
Medical-device requirements are driven by intended use, claims, jurisdiction and product characteristics—not by the presence of a heart-rate sensor, SOS button or fall-related feature alone. A watch marketed for general wellness or personal safety can have a different regulatory position from one intended to diagnose, monitor, prevent or treat a medical condition.
Review product labels, instructions, software functions, marketing copy and sales claims together. An apparently minor statement can change how the intended purpose is understood. Projects involving clinical or medical claims should receive qualified, market-specific regulatory assessment early enough to influence requirements, evidence and development controls.
For teams designing connected care programs, the device assessment should also reflect the wider workflow described in healthcare and medical wearable solutions. Product classification does not by itself demonstrate that alerts, communications, staffing and response processes are operationally suitable.
Which Supplier Documents Should Buyers Request?
Ask for an indexed evidence set rather than a compressed folder with unexplained filenames. For each applicable requirement, the supplier should identify:
- the exact product model and hardware revision;
- the radio module, antenna and supported-band configuration;
- the report, certificate, grant or declaration number;
- the issuing laboratory, certification body or responsible authority, as applicable;
- the technical test report and its tested samples;
- the Declaration of Conformity and referenced standards where required;
- the battery test summary and matching battery identity;
- material or restricted-substance declarations and their scope; and
- any conditions, limitations, expiry dates or change-notification obligations.
Cross-check names, photographs, schematics, labels, firmware references and component identifiers. Resolve gaps before approving the product configuration. Document review does not replace a broader process used to audit a wearable device manufacturer; it answers the narrower question of whether the compliance evidence matches the watch being purchased.
Build a Certification Plan Before Freezing the Product
A practical certification plan connects technical decisions to launch responsibilities. Build it in the following order:
- Confirm target markets and the intended launch sequence.
- Define intended use, users, environments and permitted product claims.
- Freeze the radio, antenna, battery, charger and key hardware configuration used for assessment.
- Map regulatory, radio, cellular, material, battery and quality-system requirements separately.
- Assign an owner for every test, declaration, submission and supplier document.
- Reserve representative samples and identify the firmware version to be tested.
- Record dependencies, review gates and evidence required before production or shipment.
- Establish change control for components, firmware, antennas, enclosure materials and suppliers.
- Assemble a launch file that matches the final manufactured and labelled product.
The plan should show assumptions and unresolved decisions. It should not promise approval dates before the responsible laboratories, certification bodies, authorities or operators have confirmed the route. For customized projects, repeat the applicability review whenever a change could affect radio behaviour, safety, intended use or document identity.
Ask a Configuration-Specific Question
The useful question is not “Which certificates come with this smartwatch?” It is “What requirements apply to this exact configuration, intended use and target market, and what evidence demonstrates conformity?” That framing exposes gaps that a generic certificate list can hide.
WearIntell can discuss the target markets, radio and battery configuration, intended use, customization scope and certification-planning inputs for an OEM or ODM smartwatch project. Final requirements and approvals remain project- and market-specific, but an early, controlled review can help the buyer plan evidence, samples and responsibilities before the design is locked.
Bring the proposed specification, market list and existing supplier evidence to that review. These inputs make it easier to identify open decisions without assuming that documents from another model cover the new project.